Cybersecurity and custom software.
Nexeth's second line of business: a team with more than seven years of experience that protects and builds. We deliver cybersecurity services in the United States, Colombia, Peru, Brazil and Mexico.
- Experience
- +7YEARSIn security and software
- Coverage
- 5COUNTRIESAcross the Americas
- Disciplines
- 2PRACTICESSecurity and engineering
- Delivery
- One teamFrom audit to code
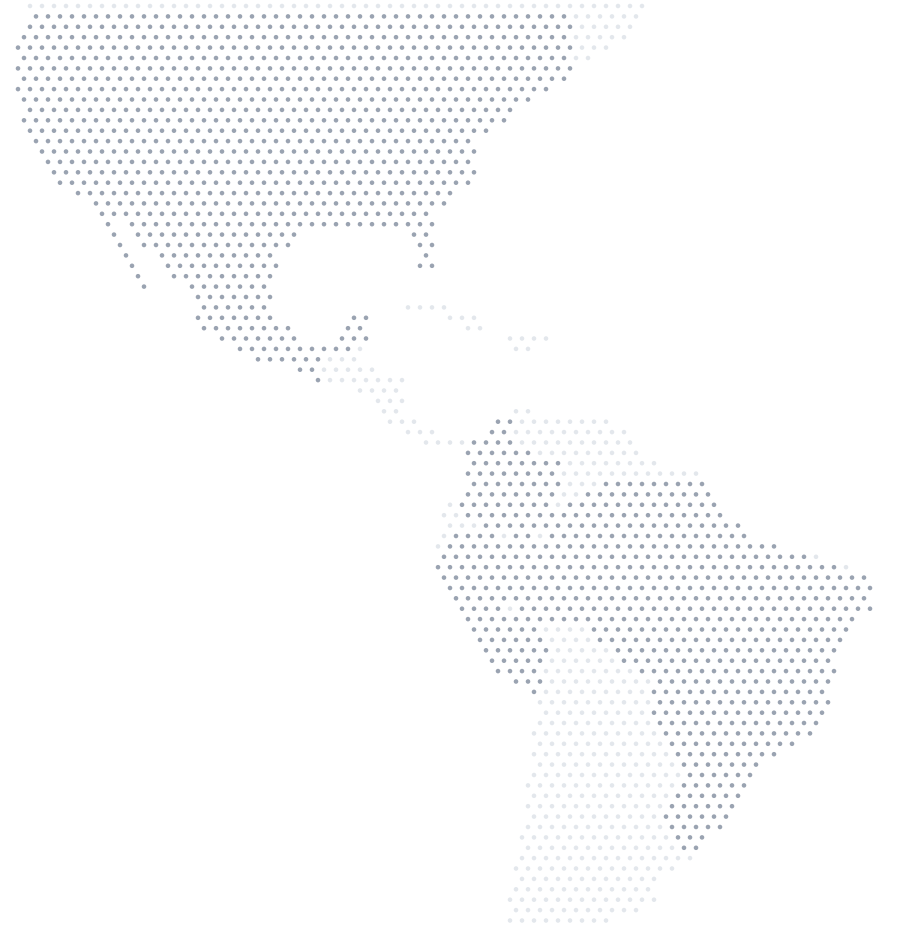
Five countries, one standard.
We work with companies in the United States, Mexico, Colombia, Peru and Brazil, with the same methodology and the same level of rigor in every market.
| Code | Country | Services |
|---|---|---|
| US | United States | Cybersecurity · Custom software |
| MX | Mexico | Cybersecurity · Custom software |
| CO | Colombia | Cybersecurity · Custom software |
| PE | Peru | Cybersecurity · Custom software |
| BR | Brazil | Cybersecurity · Custom software |
Know where you are exposed, and close it.
Six service lines, each scoped to your environment, your obligations and your risk.
Penetration testing
Controlled attacks on applications, networks and APIs to find what an attacker would find first.
Red team
Objective-driven adversary simulation that tests people, processes and technology together.
Cloud hardening
Configuration, identity and access review across your cloud environments, with fixes ranked by risk.
Incident response
Containment, investigation and recovery when something happens, with the lessons written down.
Security audits
An assessment of controls and practices against your obligations and recognized frameworks.
Ongoing support
We stay after the diagnosis: prioritization, change reviews and response when it is needed.
Software built for your operation.
We build what your company needs and deliver it ready to use, with security built in from the first day.
Custom software
Applications designed around how your company operates, not the other way around.
Integrations
We connect the systems you already use so information flows without manual re-entry.
Secure by design
Everything we build is reviewed by the same team that runs our security engagements.
What we protect and what we build is reviewed with the same rigor.
Security findings shape how we write software, and engineering experience shapes how we fix what we find.
From diagnosis to change that lasts.
Five stages, the same in every engagement and every country.
- 01
Scoping
Objectives, systems in scope, rules of engagement and timeline, agreed in writing.
- 02
Diagnosis
Testing and review of your real context: systems, team and business risk.
- 03
Prioritization
Findings ranked by what most reduces exposure or adds most value.
- 04
Remediation
We fix, or work with your team to fix, and verify every change.
- 05
Follow-up
Documented results and support so the changes hold over time.
Seven years protecting and building, with one standard.
A single team covers offensive and defensive security and software engineering. What we build is reviewed by people who test for a living, and what we find is fixed by people who build.
- Diagnosis
- We start from your real context: systems, team and business risk.
- Priorities
- First, what most reduces your exposure or adds most value to your operation.
- Delivery
- Documented results and support so the changes are sustained.
Tell us what you want to protect or build.
Company, country and a short description of the need. We reply by email with the next steps.